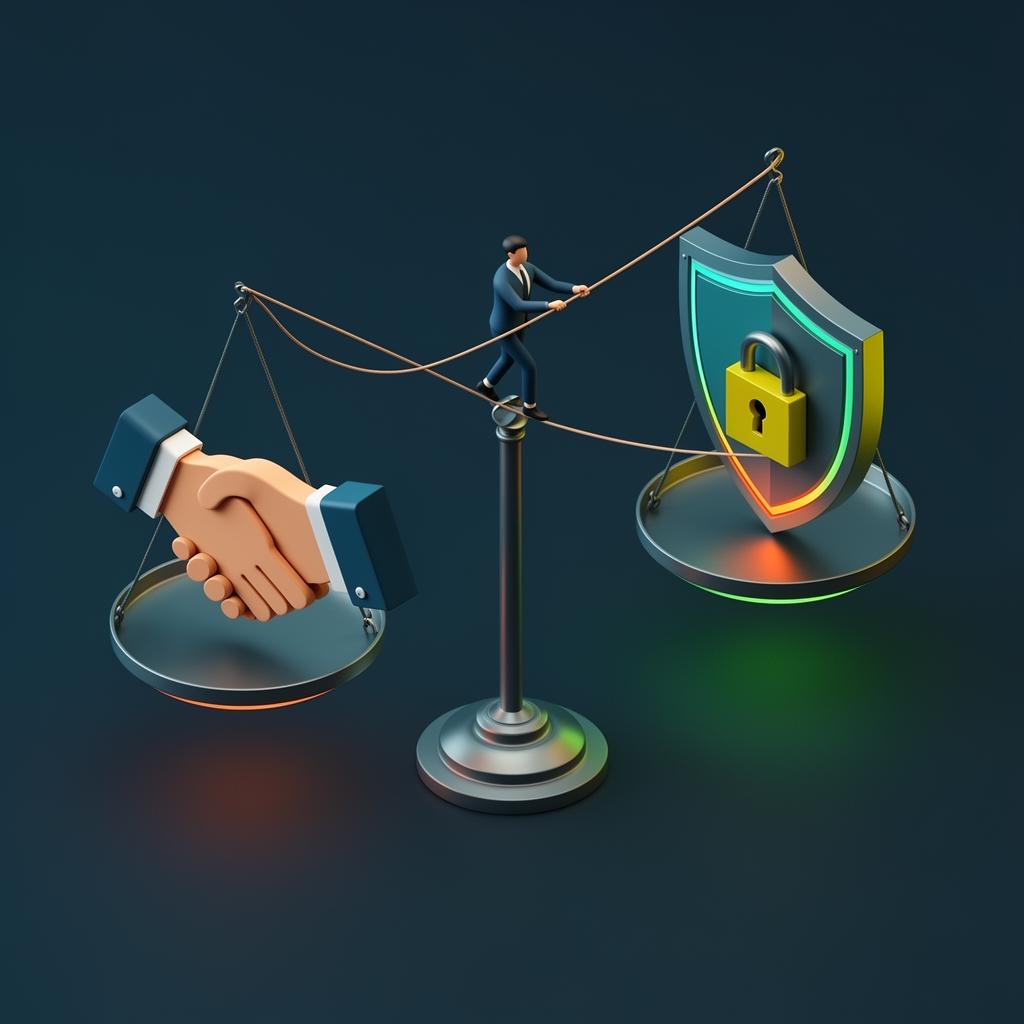
Oracle Java license Ambush Audits™, often perceived as looming risks, necessitate organizations to carefully navigate the situation as auditors delve into compliance matters. Effectively managing a Java Ambush Audit™ requires a delicate equilibrium between being affable and discreet, aiming to prevent the activation of an official audit. This blog post will explore the intricacies of Java Ambush Audits™, emphasize critical points of caution, and offer guidance on successfully navigating this complex scenario while safeguarding your organization's interests and compliance standing.
Understanding the Nature of Ambush Audits™
Java Ambush Audits™, initiated by the Oracle Java sales team, serve as a means to evaluate an organization's adherence to Oracle's licensing requirements. These audits aim to uncover potential violations or discrepancies concerning the usage of Java. A sales-led request does not, by itself, establish a contractual duty to provide deployment data. Review the applicable agreement and request with counsel to determine whether an audit clause applies and what response is required. Adept management is indispensable to avert the situation from escalating into an official audit, entailing possible legal consequences.
Key Points of Caution During an Ambush Audit™
1. Limited Disclosure
Exercise caution when providing information during a Java Ambush Audit™. Avoid sharing extensive details about your infrastructure, usage metrics, or internal processes that could be used against you. Disclose only the necessary information to demonstrate a cooperative approach.
2. Focus on Compliance Efforts
Emphasize your organization's commitment to compliance without revealing specific details that could raise suspicion or trigger an official audit. Highlight ongoing efforts such as internal reviews, policy updates, or training initiatives to showcase your dedication to meeting licensing requirements.
3. Engage Legal Counsel
Seek guidance from your legal counsel early in the audit process. They can provide valuable insights into your rights, obligations, and potential risks. Legal professionals can assist in formulating appropriate responses while safeguarding your organization's interests.
4. Internal Assessment
Conduct a thorough internal review of your Java deployments and licensing agreements before the Ambush Audit™. Identify any potential compliance issues and take proactive measures to rectify them. This proactive approach demonstrates your commitment to adhering to licensing terms. Review Oracle JDK 21 installations before applying the October 2026 update: Oracle plans to offer that update and subsequent updates under the OTN license, so confirm your entitlement and permitted use first (Oracle).
Tips for Navigating an Ambush Audit™ while Avoiding an Official Audit
1. Maintain Professionalism
Maintain a cooperative and professional tone throughout the Java Ambush Audit™ process. Respond promptly and courteously to inquiries while carefully managing the information you provide to auditors.
2. Seek Clarity
Seek clarification from the auditors regarding the purpose and scope of the Ambush Audit™. Understanding their specific concerns enables you to respond more effectively while minimizing the risk of an official audit.
3. Verify Auditor Credentials
Before sharing sensitive information, verify who is making the request and on what basis. A sales-led request does not, by itself, establish a contractual duty to provide deployment data. Review the applicable agreement and request with counsel to determine whether an audit clause applies and what response is required. Protect your organization's data by only sharing information with trusted entities.
4. Document Correspondence
Maintain comprehensive documentation of all correspondence and interactions related to the Java Ambush Audit™. Record the information you provide and document any actions to address compliance concerns. This documentation can prove valuable if an official audit is initiated subsequently.
What Should You Do Next?
- Understand your rights: A sales-led request does not, by itself, establish a contractual duty to provide deployment data. Review the applicable agreement and request with counsel to determine whether an audit clause applies and what response is required. Mishandling it can trigger a formal audit.
- Limit disclosure: Share only what's necessary to appear cooperative without exposing vulnerabilities.
- Engage legal counsel early: Get professional guidance before responding to any requests.
- Conduct an internal review: Know your Java deployment landscape before Oracle does.
- Document everything: Keep records of all communications in case the situation escalates.