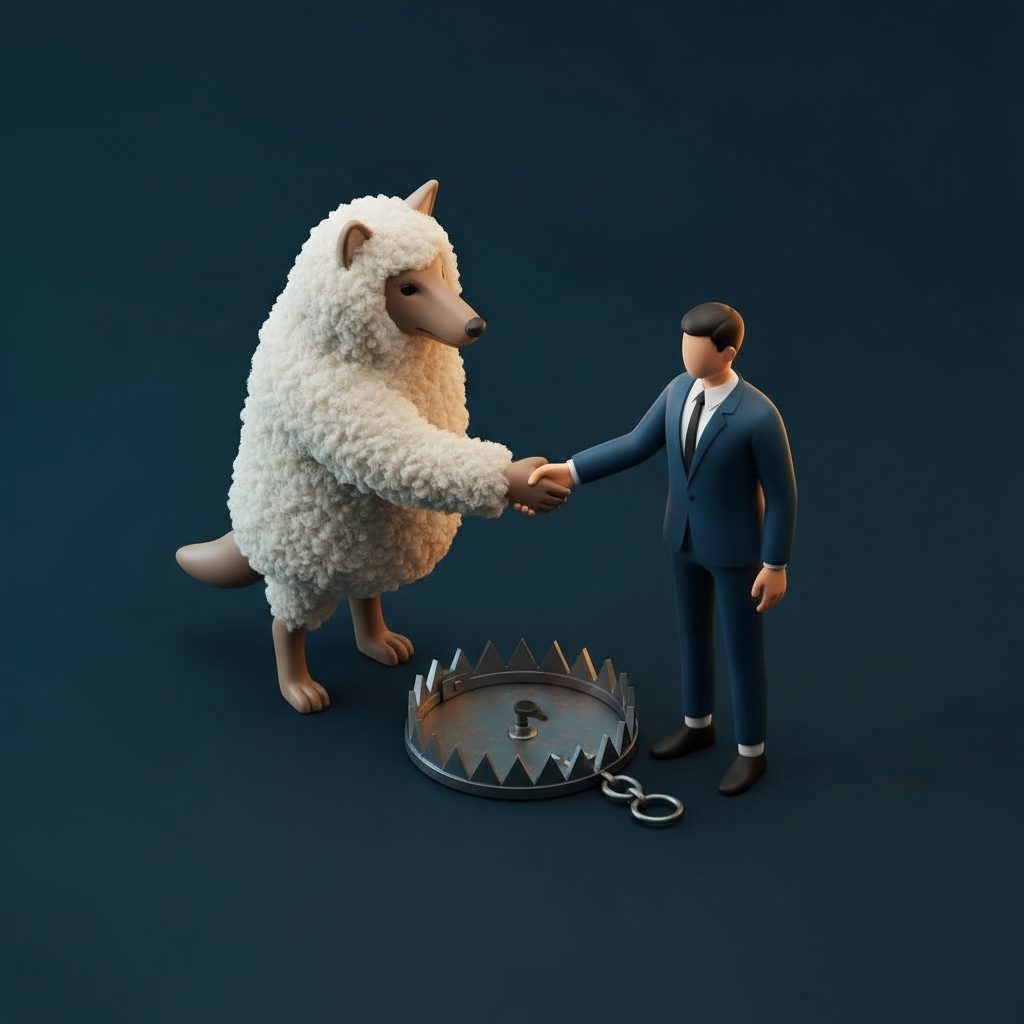
Since 2020, LicenseFortress® and the law firm Beeman & Muchmore, LLP, have been warning businesses around the world relying on Enterprise Resource Planning (ERP) software about a growing and dangerous trend among major ERP vendors: the rise of the so-called "soft audit." In multiple blogs, webinars, and published articles, we described the pernicious practice of software vendors requesting data and admissions from customers — often in the guise of a sales pitch — to extract information which is ultimately used to create software license compliance issues for the unsuspecting customer.
For example, on July 15, 2025, Michael Corey of LicenseFortress published an article in Database Trends & Applications titled Soft Audits, Hard Consequences: The Danger of Soft Audits, outlining how seemingly informal vendor inquiries can quickly escalate into material compliance exposure and significant financial liability.
But as Shakespeare once famously asked, "What's in a name?" We also asked that question about the name "soft audits," and decided that it fell far short in accurately describing a market phenomenon created by ERP software vendors that embraces the element of surprise, the suddenness of financial peril, and the outright dishonorable conduct of hiding true intentions.
There was nothing "soft" about businesses contacting us after the damage had already been done — after they had voluntarily shared with ERP software vendors detailed deployment data, architecture diagrams, virtualization configurations, or internal usage metrics, information which is later converted by the vendor into a multi-million-dollar compliance claim.
It became clear that what was going on was not a "soft audit" but rather an Ambush Audit™.
What Is an Ambush Audit™?
An Ambush Audit™ is a vendor-initiated information-gathering exercise that appears informal, collaborative, or advisory in nature — but ultimately results in a compliance claim, financial demand, or forced purchase.
Unlike a formal audit, there is:
- No official audit notice
- No defined scope
- No clear procedural boundaries
- No trigger that alerts legal or executive leadership
- No signal that the organization is in a high-risk posture
In short, the organization does not recognize that it is under examination.
That is precisely why it is so effective.
Why Ambush Audits™ Are More Dangerous Than Formal Audits
In a traditional audit:
- The company receives formal notice
- Legal counsel is engaged immediately
- Communications are centralized
- Data sharing is controlled
- The organization understands the financial risk
- Defenses go up
In an Ambush Audit™:
- The inquiry arrives as a "licensing review," "security update," "cloud optimization discussion," or "customer success check-in"
- Operational staff respond directly
- Detailed internal data is shared without legal review
- The vendor collects evidence before the company recognizes exposure
- By the time legal is involved, the vendor already possesses the data needed to construct a compliance position
The Financial Stakes Are Real
According to the Rising Cost of Software Compliance: 2025 Survey on Software Audits, 32% of audited companies pay more than $1 million to resolve audit findings.
But even that statistic understates the true impact.
The settlement check is only the visible cost. What it fails to capture are the internal resource drains, operational disruption, legal oversight, executive time, and long-term commercial concessions that often accompany an audit. The real financial exposure extends far beyond the invoice.
In fact, LicenseFortress breaks this down in more detail in its article, Software Audits Are Costing You More Than You Think — Here's Why, where we outline the hidden and secondary costs most organizations fail to model before an audit begins.
For large enterprises, those numbers escalate quickly.
When a CFO is required to authorize an unexpected seven-figure compliance payment, it is never viewed as a routine operational expense. It becomes a governance issue.
- Boards ask questions
- Audit committees get involved
- Accountability follows
And in many cases, careers are affected.
Formal Audit vs. Ambush Audit™
| Formal Audit | Ambush Audit™ | |
|---|---|---|
| Notice | Official audit notification is issued | No formal notice — inquiry arrives as a "licensing review," "security update," or "customer success check-in" |
| Scope | Defined and often contractually limited | No defined scope — any question may be posed under the guise of "assistance" |
| Procedural Guardrails | Must follow contractual audit provisions | No procedural boundaries exist |
| Timing | Often restricted; can be deferred during peak business periods | No timing restriction — can occur at any point |
| Legal Engagement | Legal counsel is engaged immediately | Legal is typically not involved until after data has been shared |
| Data Control | Data sharing is controlled and centralized | Operational staff respond directly, often sharing detailed data without legal review |
| Organizational Awareness | The organization understands the financial risk; defenses go up | The organization does not recognize it is under examination |
Many vendor agreements limit audit frequency or require reasonable scheduling. In certain industries — such as retail during peak season — organizations can often defer formal audit activity to avoid operational disruption. None of these protections apply in an Ambush Audit™.
Because the interaction is informal, organizations frequently waive the very protections that would apply in a formal audit. By the time legal is involved, the vendor already possesses the data needed to construct a compliance position.
Why This Trend Is Accelerating
Vendors have realized something critical: voluntary disclosure is more efficient than formal enforcement.
Ambush Audits™:
- Reduce vendor legal cost
- Avoid contractual restrictions
- Generate faster compliance revenue
- Shift investigative labor onto the customer
From a vendor perspective, it is highly effective. From a governance perspective, it is extremely risky.
What CIOs, CFOs, and Procurement Leaders Should Do Now
- Treat unsolicited licensing inquiries as potential audit activity
- Centralize vendor communications involving licensing or deployment data
- Require legal review before sharing architecture diagrams, virtualization details, or usage metrics
- Establish a formal internal audit-response protocol — even for informal inquiries
- Educate operational IT staff on the financial implications of oversharing
- Engage independent expertise early
When significant licensing exposure is possible, outcomes improve materially when experienced software compliance specialists and legal counsel with deep domain expertise are involved at the outset.
According to the Rising Cost of Software Compliance: 2025 Survey on Software Audits, 95% of respondents reported that engaging a third-party advisory firm helped reduce their audit liability.
That statistic should not be surprising.
Software licensing is contractual law layered on top of technical architecture. Most internal IT and procurement teams manage licensing operationally — but audit defense is a specialized discipline. It requires understanding vendor tactics, contractual leverage points, negotiation strategy, and forensic data control.
Engaging qualified experts early is not an admission of noncompliance. It is a governance decision — one that protects financial exposure, preserves negotiation leverage, and signals executive oversight.
For a comprehensive breakdown of Ambush Audit™ tactics, real-world examples, and a step-by-step response framework, visit our dedicated Ambush Audits™ Resource Center.
Final Thought
The danger is not the formal audit you see coming.
The danger is the one you don't recognize until it is too late.
The industry may call it a "soft audit."
We call it what it truly is:
An Ambush Audit™.
And organizations that fail to treat it accordingly are exposing themselves to unnecessary and avoidable financial risk.
Ambush Audit is a registered trademark of LicenseFortress, Inc., and Beeman and Muchmore, LLP.
© 2026 LicenseFortress, Inc. / Beeman & Muchmore, LLP. Unauthorized use and/or duplication of this material without either express and written permission from this site's author and/or owner, or explicit attribution by way of website links to LicenseFortress, Inc. and Beeman & Muchmore, LLP, is strictly prohibited.