What Is Proactive Software Audit Risk Prevention?
Proactive software audit risk prevention means addressing licensing compliance gaps before a vendor initiates an audit. Instead of reacting to an audit notice, organizations regularly assess their software deployments against contractual entitlements and remediate discrepancies while they still control the timeline.
A software audit notice from Oracle, Microsoft, IBM, or VMware can arrive without warning—and once it does, your options narrow quickly. Proactive software asset management (SAM) gives organizations visibility before that moment, helping them identify compliance gaps and reduce audit exposure on their own terms.
As LicenseFortress discussed previously in 7 Reasons Why Waiting for an Oracle Audit is the Wrong Approach, organizations that wait passively for vendor audits often lose negotiation leverage, visibility, and control long before the audit formally begins.
Rising subscription costs, Oracle Java licensing changes, VMware by Broadcom transitions, cloud migration complexity, and increasingly aggressive vendor enforcement have pushed proactive SAM from a back-office IT function into a strategic risk-management discipline.
This article explains what proactive SAM looks like in practice. You'll learn how to spot the leading indicators that signal audit risk, the internal controls that keep you compliant, and the ongoing practices that make audit readiness a routine part of your operations rather than a crisis response.
Key Takeaways: How Proactive SAM Prevents Software Audit Claims
- Proactive SAM identifies compliance gaps before vendors do, giving you time to remediate on your own terms.
- Leading indicators like contract changes, virtualization updates, and support reductions often trigger vendor scrutiny.
- Internal controls such as centralized license tracking and regular audits create defensible documentation.
- Vendor-independent SAM helps organizations evaluate licensing obligations without incentives tied to software sales.
- Ongoing monitoring and entitlement reconciliation turn audit readiness into a repeatable business process rather than emergency response.
Why Do Vendors Audit and How Can You Stay Off Their Radar?
Vendors do not audit randomly. Their audit programs target accounts where commercial intelligence suggests a high likelihood of finding compliance gaps.
Understanding what triggers vendor interest helps organizations reduce their profile as an audit target.
Common Audit Triggers
Several events consistently draw vendor attention.
Mergers and acquisitions create licensing chaos because entitlements rarely transfer cleanly. Reductions in support spend or contract terminations can signal disengagement that vendors investigate further. Virtualization platform changes—especially involving VMware, Hyper-V, cloud migrations, or hybrid infrastructure—can dramatically change licensing exposure in ways many organizations miss.
Even routine infrastructure upgrades can create unexpected licensing consequences. A hardware refresh with higher-core processors or cloud scaling changes may increase license requirements without the organization realizing it.
Organizations also underestimate how frequently vendors use "soft touch" engagement to gather audit intelligence before a formal notice occurs.
Increased deployment-data requests, licensing workshops, "optimization reviews," or sudden involvement from vendor licensing specialists can all signal elevated audit interest months before an official audit begins.
LicenseFortress refers to many of these early-stage activities as Ambush Audits™ because they frequently collect the same deployment intelligence used during formal compliance reviews.
What Are the Leading Indicators of Audit Risk?
Leading indicators are the early warning signs that an organization may face elevated audit scrutiny. Recognizing these signals gives organizations time to act before a formal notice arrives.
Internal Warning Signs
Watch for:
- Incomplete software inventories
- Scattered license documentation
- Inconsistent entitlement tracking
- Unclear software ownership
- Decentralized procurement
- Shadow IT deployments
If your procurement or IT teams cannot quickly answer how many licenses you own versus how many are deployed, you likely have a visibility problem.
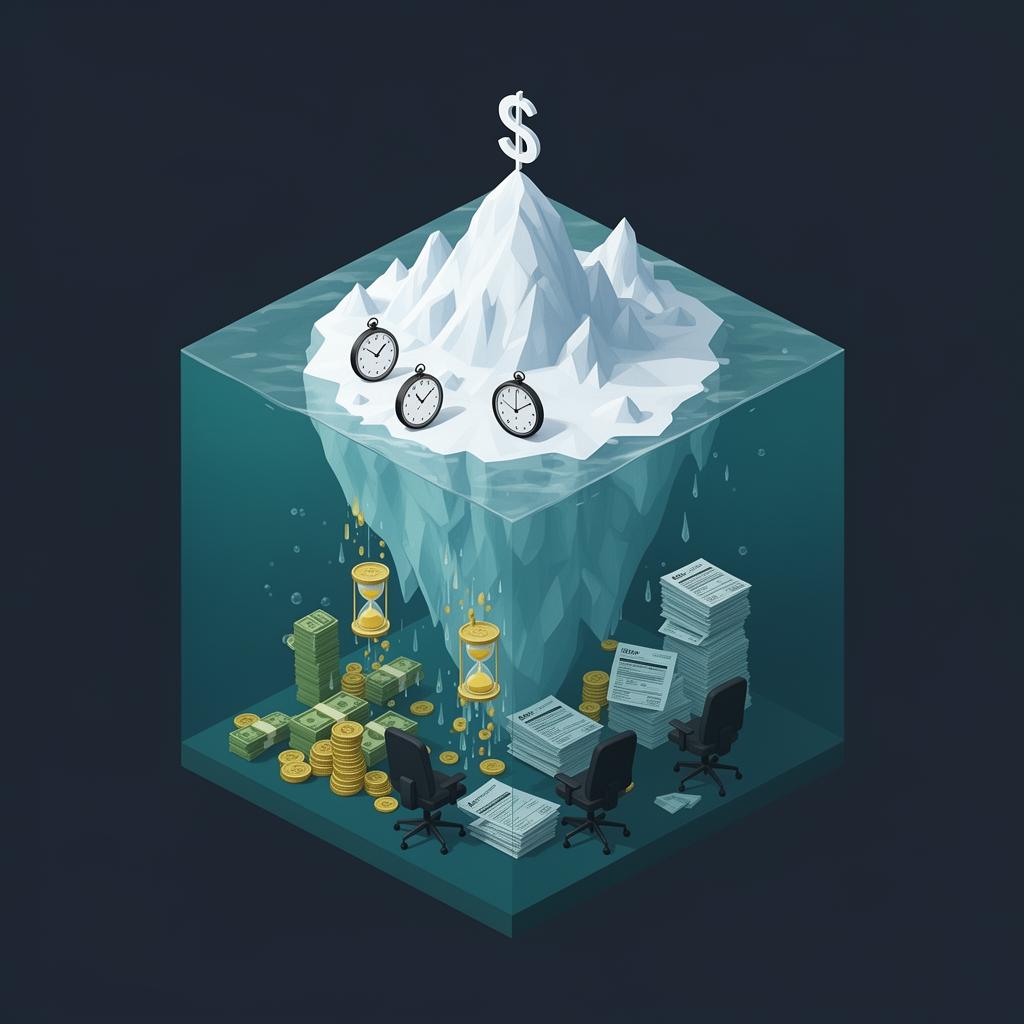
Most compliance problems are not caused by intentional misuse. They emerge gradually through infrastructure modernization, cloud migration, virtualization changes, mergers, feature enablement, and decentralized deployment activity.
This "compliance drift" is one reason point-in-time compliance assessments often become outdated quickly without continuous monitoring.
External Warning Signs
Pay attention when vendors:
- Increase deployment-data requests
- Request architecture diagrams
- Propose "health checks"
- Push optimization workshops
- Introduce licensing specialists into routine calls
- Escalate contract conversations unexpectedly
These interactions often occur well before a formal audit notice arrives.
LicenseFortress helps organizations interpret these vendor behaviors and assess whether they represent routine engagement or elevated audit risk.
Which Internal Controls Reduce Software Licensing Compliance Risk?
Internal controls create the documentation and governance processes that establish defensible compliance positions.
When built correctly, these controls give organizations confidence during renewals, audits, and vendor negotiations.
Centralized License Tracking
A centralized system that tracks:
- Software entitlements
- Contracts
- Purchase history
- Deployments
- Renewal dates
is foundational to proactive SAM.
Organizations need a single source of truth showing:
- What they own
- What is deployed
- Where gaps exist
- Which environments create exposure
This often requires aggregating information across procurement systems, cloud platforms, discovery tools, and vendor portals.
Regular Internal Compliance Reviews
Organizations should conduct internal compliance reviews on a recurring basis—quarterly for high-risk vendors like Oracle and Microsoft, and at least annually for others.
These reviews compare deployed software against contractual entitlements and identify discrepancies before vendors discover them.
LicenseFortress Compliance & Optimization Reviews (COR) help organizations establish defensible Effective License Positions and audit-ready documentation before a vendor controls the process.
Clear Ownership and Accountability
Every major software publisher should have designated internal ownership responsible for:
- Usage oversight
- Entitlement management
- Renewal governance
- Compliance tracking
Without clear ownership, licensing responsibilities fall between procurement, IT, infrastructure, and finance teams.
That fragmentation creates risk.
How Does Ongoing SAM Practice Maintain Audit Readiness?
Audit readiness is not a one-time project.
The organizations that handle audits effectively are rarely the ones scrambling after the audit notice arrives. They are the organizations that established visibility, monitoring, and defensible licensing positions long before the vendor initiated the review.
License Monitoring and Entitlement Reconciliation
Organizations should monitor software usage regularly to identify:
- New deployments
- Infrastructure changes
- Unused licenses
- Feature enablement
- Cloud expansion
- Virtualization drift
Entitlements should be reconciled against deployments at least quarterly.
Organizations with documented entitlement visibility and defensible Effective License Positions are generally in a much stronger position during renewals, audits, and vendor negotiations because they understand their exposure before the vendor defines it for them.
Contract and Renewal Management
Organizations should actively manage:
- Contract terms
- Renewal timelines
- Licensing metrics
- Cloud-use rights
- Virtualization restrictions
- Audit clauses
Many vendors increasingly use renewals to reshape historical licensing rights, introduce subscription transitions, or expand reporting obligations.
The LicenseFortress Oracle Negotiation Guide provides additional guidance on managing enterprise software renewals strategically.
Documentation Discipline
Organizations should maintain:
- Proof-of-entitlement records
- Purchase documentation
- Vendor correspondence
- Contract amendments
- Licensing assumptions
- Architecture documentation
The goal is to establish a defensible Effective License Position (ELP) that can be produced confidently if audit scrutiny occurs.
How Does LicenseFortress Help Prevent Software Audit Claims?
LicenseFortress takes a proactive approach to software asset management that combines licensing expertise, legal coordination, and continuous monitoring.
Unlike vendor-aligned consultants or software resellers, LicenseFortress operates independently—focused entirely on protecting the customer's interests.
ArxPlatform® provides organizations with continuous visibility into software deployments and license positions across Oracle, Microsoft, IBM, VMware, SAP, and other major publishers.
ArxAware® compliance alerts notify organizations when compliance drift occurs so remediation can happen before exposure escalates.
This ongoing monitoring turns audit readiness into a repeatable operational process rather than a periodic fire drill.
When audits do occur, LicenseFortress Audit Defense services combine licensing specialists, infrastructure expertise, and legal coordination to help organizations challenge unsupported claims and negotiate from a position of knowledge.
In Conclusion: Build Audit Readiness Before You Need It
Proactive SAM prevents software audit claims by giving organizations visibility, control, and documentation before vendors come knocking.
The leading indicators are often visible months before a formal audit notice arrives—if organizations know what to look for.
Internal controls turn compliance from guesswork into documented fact.
Ongoing monitoring prevents compliance drift from quietly escalating into major financial exposure.
And organizations with defensible licensing positions are generally in a much stronger position during audits, renewals, and vendor negotiations because they understand their exposure before the vendor defines it for them.
The organizations that handle audits smoothly are rarely the lucky ones.
They are the prepared ones.