Software compliance has traditionally been viewed as a procurement or finance responsibility. But as organizations adopt hybrid cloud, AI-powered services, virtualization, and increasingly complex software agreements, software licensing is becoming an enterprise security and governance issue as well.
Security leaders today are responsible for protecting far more than endpoints and networks. They help manage vendor risk, cloud governance, data privacy, regulatory compliance, and operational resilience. Software compliance intersects with every one of those responsibilities.
Poor visibility into software deployments can leave unauthorized applications running in production. Vendor audit requests often require organizations to share detailed infrastructure information. Telemetry collected by enterprise software may raise data governance questions. Complex licensing rules influence cloud architecture decisions. Even routine security patching can unintentionally enable licensable features.
None of these issues replace traditional cybersecurity concerns — but they do create additional operational, contractual, and regulatory risks that security teams increasingly help manage.
This guide introduces six areas where software compliance and security overlap and provides a Software Compliance & Security Risk Matrix to help organizations prioritize their exposure. Each section links to more detailed guidance for teams looking to explore a specific topic.
Where Software Compliance Creates Security Risk
1. Limited Software Visibility Creates Security Blind Spots
Security teams cannot protect software they don't know exists.
Shadow IT, unauthorized installations, forgotten virtual machines, dormant SaaS subscriptions, and cloud resources created outside normal governance processes all reduce visibility across the environment. These deployments frequently escape both software asset management and security monitoring.
The consequences extend beyond licensing. Unsupported software may miss critical security updates, unnecessary privileged accounts remain active, and organizations lose confidence in the accuracy of their software inventory during both audits and incident response.
Improving software visibility strengthens both compliance and security.
Learn more: The Hidden Security Risks of Poor Software Compliance
2. Vendor Audits Can Expose More Than Licensing Information
Software audits are often viewed as financial events, but they also involve the exchange of detailed technical information.
Vendors may request deployment inventories, virtualization layouts, infrastructure diagrams, discovery tool outputs, cloud configurations, and other operational data to validate licensing positions. While these requests are common, organizations should carefully understand what information is being shared, why it is being requested, and what contractual obligations require its disclosure.
Security, legal, procurement, and software asset management teams should work together before responding to audit requests to ensure information is accurate, appropriately scoped, and aligned with contractual requirements.
Learn more: How to Respond to Software Deployment Data Requests and Stop Oversharing Data With Oracle
3. Security and Compliance Teams Need Shared Ownership
Software compliance no longer belongs exclusively to procurement or IT asset management.
Cloud operations, security architecture, procurement, legal, IT operations, and software asset management all influence licensing outcomes. Decisions made by one team often create risk for another.
Examples include:
- Infrastructure teams deploying new virtualization platforms
- Cloud teams migrating workloads between providers
- Security teams enabling new platform features
- Procurement negotiating enterprise agreements
- Legal reviewing contractual language
- SAM teams monitoring entitlement and usage
Organizations with clearly defined ownership across these functions are generally better prepared for audits, cloud migrations, and vendor negotiations than those operating in isolated silos.
Learn more: Why Compliance and Security Teams Must Work Together and Governance & Control: The Backbone of Trust in SAM
4. Data Privacy Extends Beyond Customer Information
Enterprise software increasingly collects diagnostic information, usage analytics, telemetry, and operational metrics.
While these capabilities often improve product performance and vendor support, they also introduce important governance questions:
- What information is collected?
- Where is it stored?
- Who can access it?
- How long is it retained?
- Does it create additional regulatory obligations?
For organizations operating under GDPR, CCPA, HIPAA, or other regulatory frameworks, software telemetry should be evaluated alongside other data governance practices rather than treated as a separate licensing concern.
Learn more: The Paradox of Trust: Software Asset Management and Data Privacy and How AI Is Creating New Audit Opportunities for Software Vendors
5. AI Is Expanding Both Security and Compliance Considerations
Enterprise software vendors are rapidly introducing AI assistants, copilots, embedded machine learning, vector databases, and new consumption-based licensing models.
These capabilities create opportunities for productivity — but they also introduce new governance questions.
Security teams should understand:
- Where AI features process organizational data
- What telemetry is collected
- How AI workloads affect software deployments
- Whether new licensing metrics apply
- How AI services integrate with existing security controls
Organizations should evaluate AI adoption from both a security and software governance perspective before enabling new capabilities at scale.
Learn more: Why LicenseFortress Isn't Embedding AI Throughout Its SAM Platform — Yet and Why AI Is Driving Database Costs Higher Than Expected
6. Security Changes Can Have Licensing Consequences
Security updates occasionally introduce licensing considerations that organizations may overlook.
Oracle's Critical Patch Updates (CPUs), for example, sometimes include changes that interact with optional database features or new product capabilities. Infrastructure changes made to improve security can also affect virtualization boundaries, cloud configurations, or processor licensing calculations.
Security teams should understand when operational changes could have downstream licensing implications and involve software licensing specialists when significant platform changes are planned.
Learn more: Oracle October 2025 CPU Compliance Risks
Software Compliance & Security Risk Matrix
Not every software compliance issue carries the same level of organizational risk.
Some primarily affect software spend. Others introduce operational complexity, reduce security visibility, increase regulatory exposure, or strengthen vendor leverage during audits.
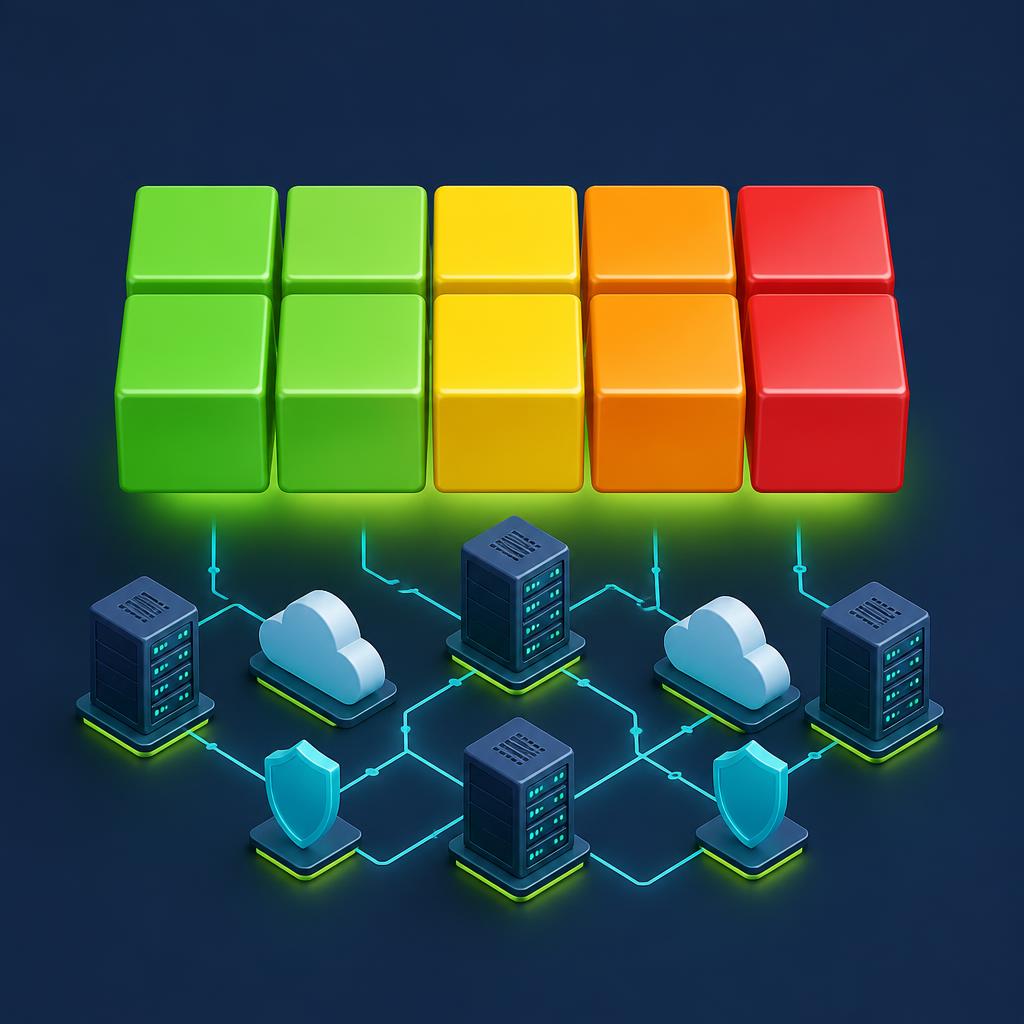
The matrix below provides a practical framework for evaluating where software compliance creates the greatest security and governance risk — and where remediation efforts should be prioritized first.
| Risk Level | Risk Category | Threat | Vendors Most Affected | Mitigation Strategy |
|---|---|---|---|---|
| Low | Overprovisioned & inactive licenses | Excess spend, expanded attack surface | Microsoft, IBM, Quest, Micro Focus | License rationalization and periodic usage audits |
| Low | True-ups & vendor pricing shifts | Unexpected renewal costs, budget shock | Microsoft, IBM, SAP | Proactive contract negotiation and cost forecasting |
| Moderate | Lack of visibility across IT | Poor decisions, compliance failure | All vendors | Integrated SAM and IT asset management |
| Moderate | Third-party SaaS & licensing risks | Compliance gaps, surprise vendor charges | Quest, Micro Focus, Microsoft | Centralized SaaS license tracking |
| Moderate | Unauthorized software use | Shadow IT, unpatched vulnerabilities, compliance risk | Oracle, Microsoft, IBM, SAP, VMware, Quest, Micro Focus | Access controls, SAM monitoring, endpoint policies |
| High | Vendor audits & compliance gaps | Untracked licenses, audit fees, IT risk exposure | Oracle, IBM, Microsoft, SAP, Quest | Continuous tracking and pre-audit readiness |
| High | Hybrid & multi-cloud compliance | Inconsistent security policy, audit risk | Oracle, VMware, Microsoft, IBM | Unified compliance framework and automated policy enforcement |
| High | Cloud & virtualization complexity | Misconfigured deployments, breaches, over-licensing | VMware, Microsoft, Oracle, IBM | Licensing optimization and vendor-approved configurations |
| Critical | Non-contractual policies | Vendors enforcing policy as contract to drive spend | Oracle (partitioning), Microsoft (virtualization), SAP (indirect access) | Legal-backed contract review and challenge strategy |
| Critical | Data privacy & regulatory risk | Vendor telemetry exposing GDPR / CCPA / HIPAA violations | Microsoft, Oracle, SAP, IBM | Contractual data protections and compliance oversight |
How Security Teams Can Use This Matrix
The matrix is intended to support conversations across security, IT operations, procurement, legal, and software asset management — not replace detailed risk assessments.
Use it to:
- Identify software compliance issues that also create security or governance exposure.
- Prioritize remediation based on operational, regulatory, and contractual impact — not just licensing cost.
- Assign clear ownership across security, procurement, IT operations, legal, and SAM teams.
- Support cloud migrations, AI initiatives, and software modernization projects by identifying licensing risks before deployment.
- Prepare for vendor audits by understanding where technical and contractual exposure overlap.
- Revisit the assessment regularly as cloud services, AI capabilities, and vendor licensing models evolve.
The Bottom Line
Software compliance has evolved far beyond counting licenses.
Today it influences cloud architecture, software governance, vendor risk, data privacy, AI adoption, and operational security. While software licensing is not a cybersecurity discipline, the decisions organizations make around software deployment increasingly affect the broader security and governance posture of the enterprise.
Organizations that manage software compliance proactively are better positioned to reduce audit exposure, strengthen operational visibility, support regulatory obligations, and make informed technology decisions.
The articles linked throughout this guide explore each of these areas in greater depth and provide practical recommendations for reducing software compliance risk while strengthening enterprise security governance.
Want to pressure-test your compliance strategy against this matrix? Book a meeting and we'll walk through your highest-risk rows together.